Network Security
Security in layers — because one control is never enough.
I harden networks the way incidents actually happen: perimeter, access paths, segmentation, and monitoring that still helps when one piece fails.
Protect the path from the internet to your workloads.
Prevention, segmentation, encryption, and detection — sized to the environment you already run.
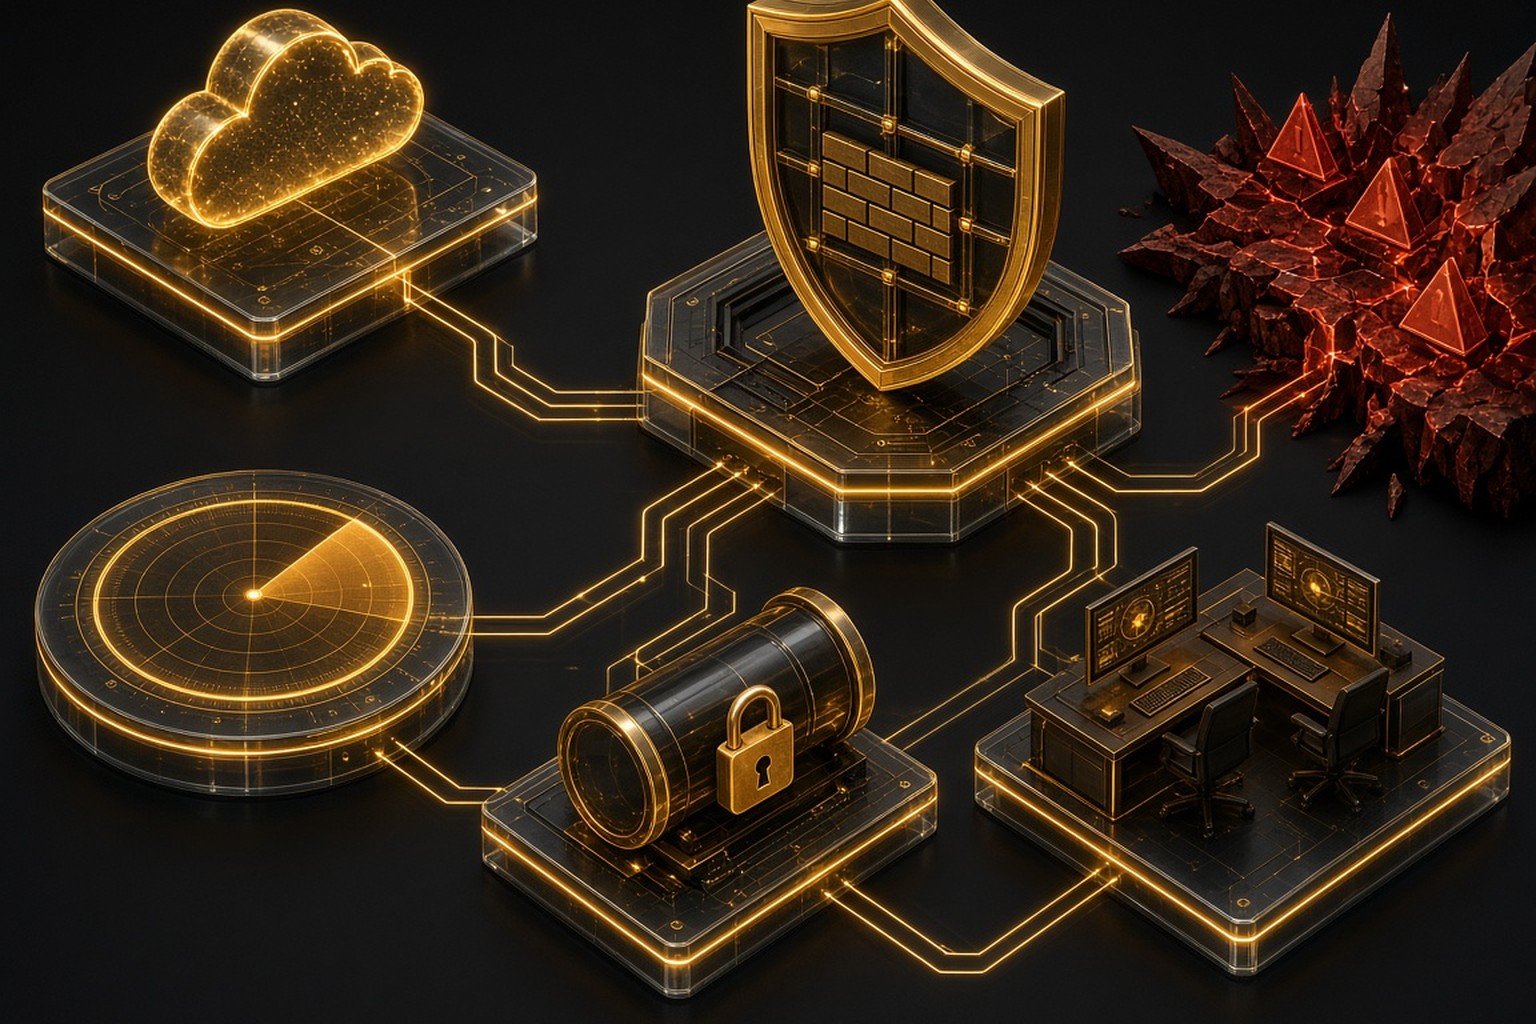
Security Flow
How traffic is protected before it reaches your systems
Security Approach
Every network engagement starts with an audit of exposure: open ports, weak access rules, unpatched services, and unmonitored traffic. From there I apply the minimum set of controls needed to close real gaps without adding unnecessary complexity.
What This Covers
- Perimeter and internal firewall policy design
- Secure remote access and VPN configuration
- Continuous traffic monitoring and alerting
- Incident response and recovery planning
Firewall Configuration
Perimeter and host-level rules built around least privilege
VPN & Secure Tunnels
Encrypted site-to-site and remote access connectivity
Intrusion Detection & Prevention
IDS/IPS tuning to catch and block malicious traffic
Network Segmentation
VLANs and zoning to contain breaches and limit blast radius
SSL/TLS & Encryption
Certificate management and encrypted data in transit
Threat Monitoring
Log analysis and alerting for early detection of anomalies